SaaS Vendor Merger Acquisition Impact on Contracts
The SaaS vendor merger acquisition impact on contracts is rarely limited to a new logo or billing entity. A merger or acquisition can affect service levels, support obligations, pricing, data processing, subprocessors, security controls, and your ability to exit. The practical question is not simply whether the contract survives. It is whether the post-transaction vendor remains the same risk profile you approved.
For buyers, the strongest protection comes from combining change-of-control rights with specific SLA, data, notice, and transition obligations in the MSA.
What happens to a SaaS contract after a merger or acquisition?
A SaaS contract may continue automatically after an acquisition, but the legal and operational result depends on the transaction structure and the contract language. A stock purchase or merger may leave the original contracting entity in place, while an asset purchase may require assignment or customer consent.
That distinction matters because “the contract remains active” does not necessarily mean the service remains materially unchanged. The acquiring company may alter:
- The hosting environment or data-processing locations
- The support organization and escalation path
- Product priorities, roadmap, or integrations
- Subprocessors and security controls
- Pricing, packaging, renewal terms, or usage metrics
- The entity responsible for indemnities and liability obligations
The American Bar Association identifies service continuity, data ownership, security, termination, and transition assistance as core SaaS contracting issues. It also notes that customers should receive notice of material service changes and may need a penalty-free termination right when those changes are significant. (americanbar.org)
Which contract risks should buyers review first?
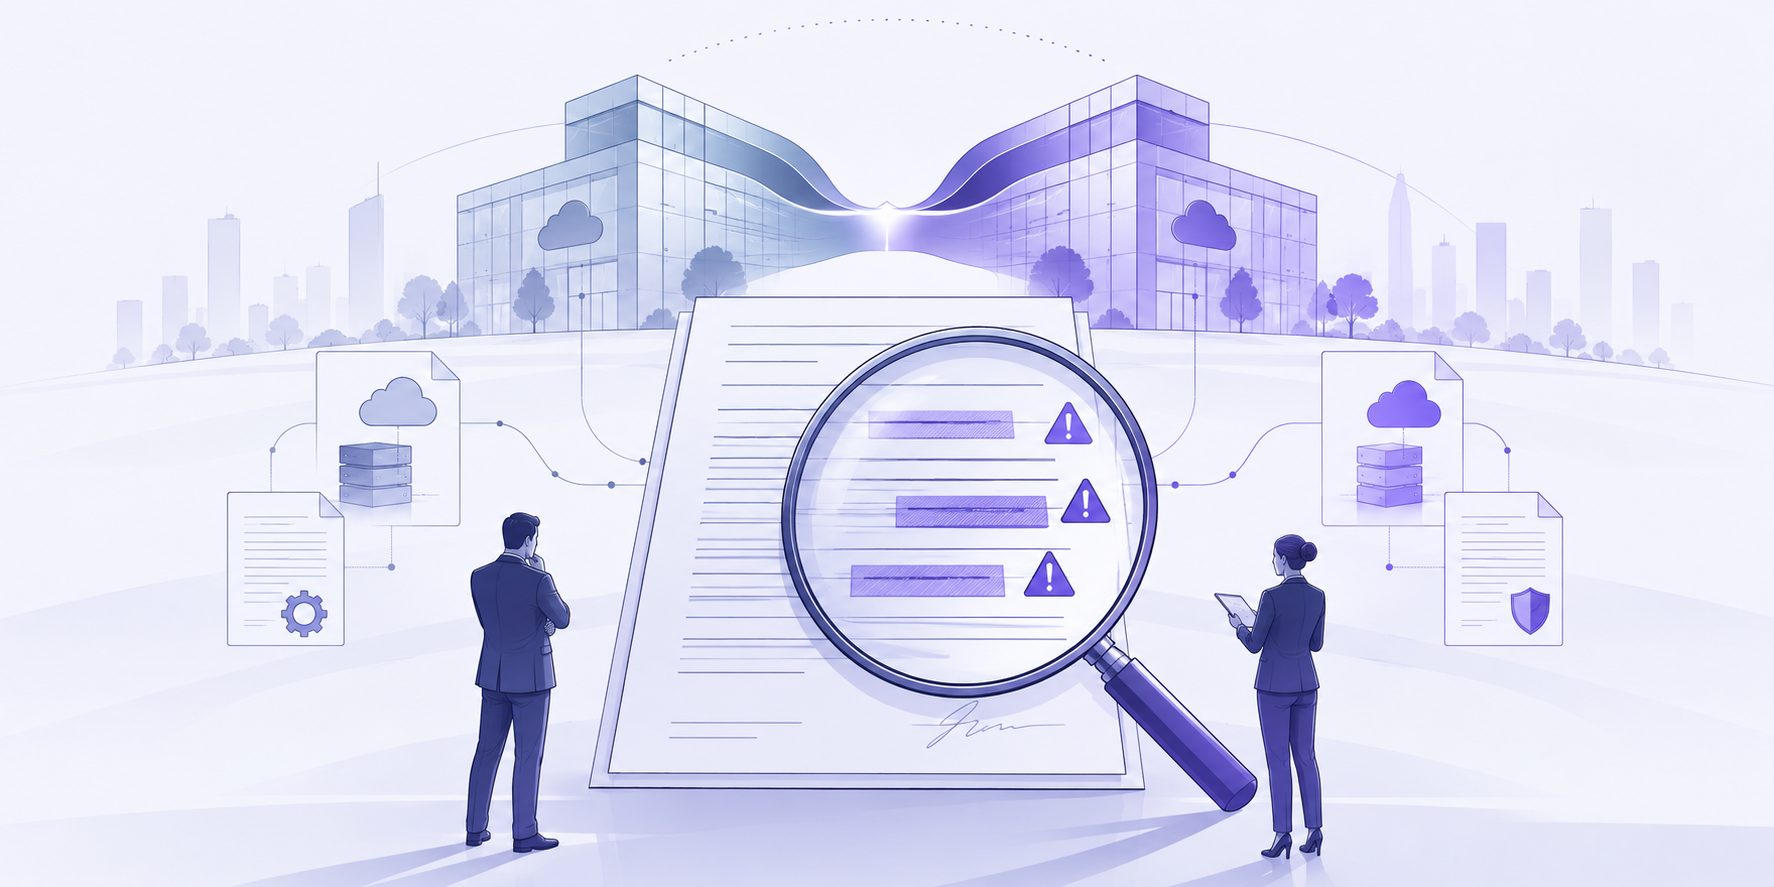
The fastest way to assess acquisition exposure is to review the agreement in five layers: legal control, service performance, data governance, economics, and exit capability.
| Review area | Acquisition-related risk | Buyer protection |
|---|---|---|
| Change of control | New owner inherits the relationship without meaningful customer input | Notice, consent, or termination right |
| SLA and support | Service levels or escalation resources decline | SLA continuity and material-change remedy |
| Data and privacy | New affiliates, subprocessors, or processing purposes gain access | Purpose limitation and approval rights |
| Pricing | Packaging, renewal price, or minimum commitments change | Price protection and renewal controls |
| Exit | Data export becomes slow, expensive, or technically incomplete | Structured transition assistance and deletion certificate |
Change of control and assignment
A conventional assignment clause may not cover every acquisition. Some transactions change ownership without formally assigning the agreement. A well-drafted clause should define change of control separately from assignment and specify the trigger, such as a sale of a majority interest, merger, or transfer of substantially all relevant assets.
The buyer should also distinguish between:
- A low-risk internal reorganization
- An acquisition by an affiliate with equivalent financial and compliance characteristics
- A sale to a third party with a materially different risk profile
A useful compromise is to permit assignment to an affiliate or successor only if the successor assumes all obligations, maintains materially equivalent security and service commitments, and does not materially reduce the vendor’s ability to perform.
SLA and support continuity
An acquisition can leave uptime unchanged while weakening the support model that makes the platform usable. Watch for changes in named escalation contacts, support hours, response targets, incident communications, and the vendor’s ability to meet recovery objectives.
Your MSA should state that the vendor must continue meeting the existing SLA during the transaction and transition period. If the acquired product is integrated into another platform, define what counts as a material degradation, including:
- Lower uptime or slower response times
- Reduced support coverage
- Removal of a critical integration
- Loss of a contractual security certification
- Delayed incident notification
- Discontinuation of a feature required by a documented business process
For negotiation benchmarks, compare the agreement against a practical SaaS vendor SLA response time framework rather than accepting “commercially reasonable efforts” as the only service commitment.
How can an acquisition increase data and security risk?
An acquisition can expand who controls, processes, or accesses customer data. The risk is not limited to a data breach. It also includes a new parent company using data for analytics, product development, cross-service profiling, or AI model training beyond the original commercial purpose.
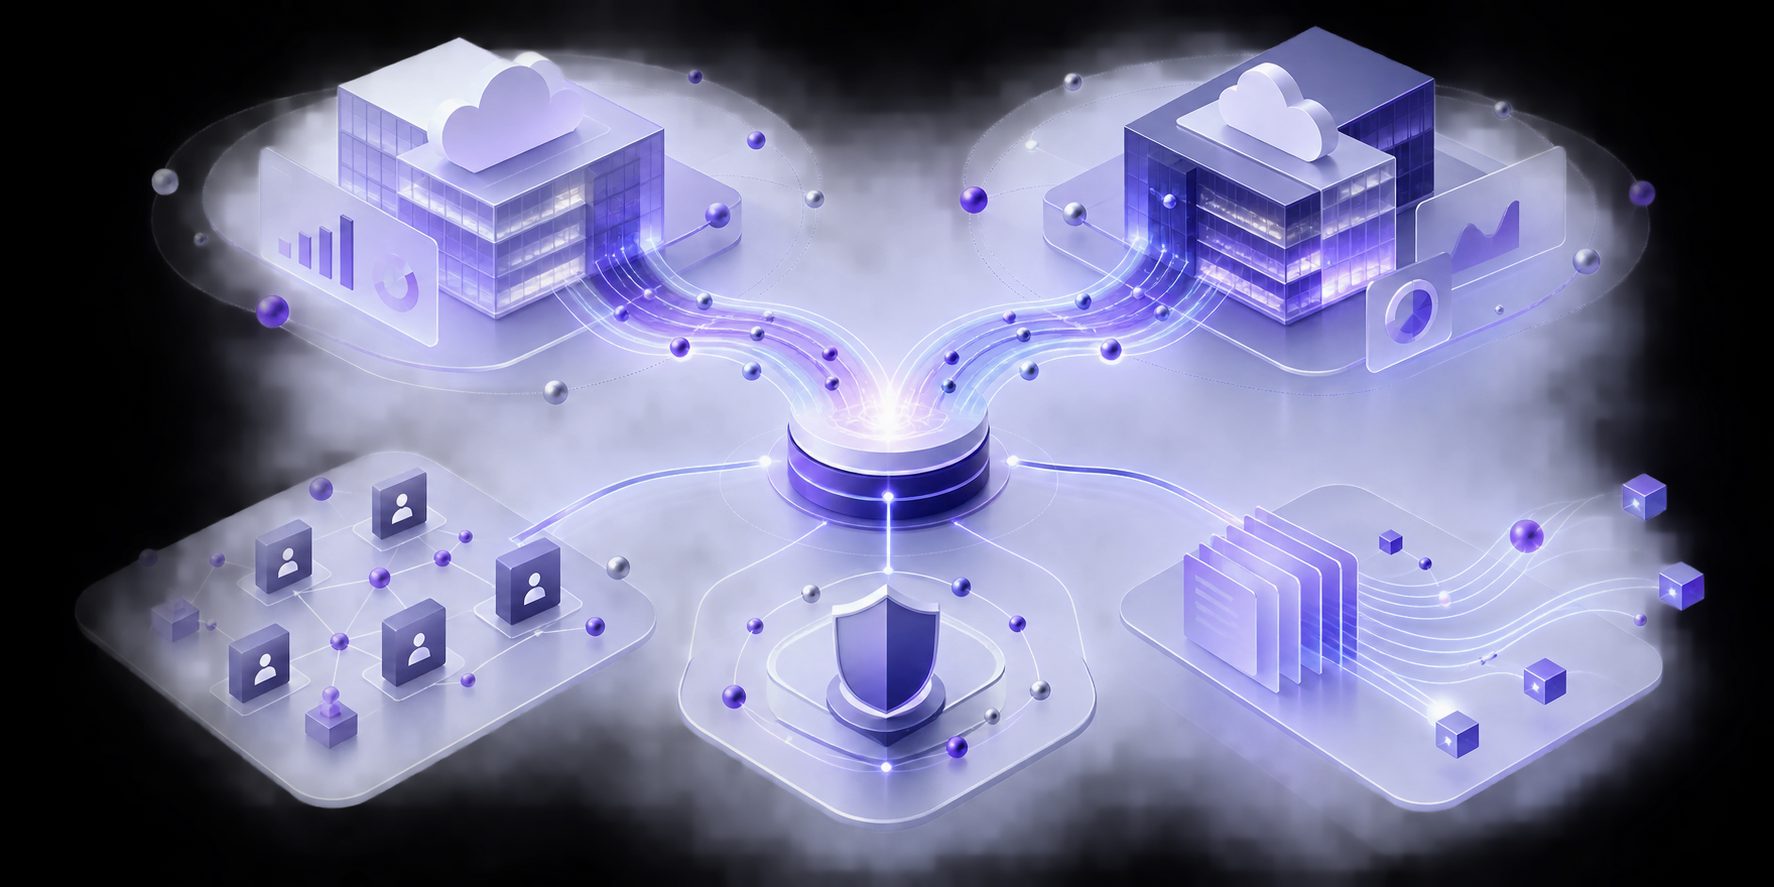
The MSA and DPA should address:
- Customer ownership of customer data
- Permitted processing purposes
- Affiliate and parent-company access
- Hosting locations and transfer mechanisms
- Subprocessor notice and objection rights
- Encryption and access-control requirements
- Security incident notification deadlines
- Return, export, and deletion procedures
- Restrictions on de-identification, aggregation, and model training
A recent analysis of SaaS M&A data issues emphasizes that transition arrangements should cover data access, security, incident response, subprocessors, deletion, and exit support—not merely the transfer of the customer list. (matchpoint-partners.com)
What should a buyer put in a change-of-control clause?
A buyer-friendly clause should create a controlled decision process rather than an automatic right to cancel every time the vendor reorganizes.
Recommended clause components
- Defined trigger: Identify merger, sale of voting control, asset sale, or other transaction that materially changes ownership or control.
- Advance notice: Require written notice within a defined period, such as 30–60 days before closing when disclosure is legally permitted.
- Information rights: Require details about the successor entity, service continuity, data processing, security posture, and support model.
- Assumption of obligations: Make the successor expressly assume the MSA, SLA, DPA, indemnities, confidentiality obligations, and transition duties.
- Material-change remedy: Permit termination if the transaction causes a material adverse change to service, security, compliance, ownership, or commercial terms.
- Data protection condition: Prevent expanded data use or new subprocessors unless permitted by the DPA and applicable law.
- Transition assistance: Require usable export formats, reasonable technical support, continued access during migration, and deletion confirmation.
- No punitive exit fee: Avoid termination charges when the buyer exits because of a qualifying change of control or material adverse change.
A concise model concept is:
If a change of control results in a material adverse change to the Services, security controls, data-processing practices, support obligations, or the customer’s commercial rights, the customer may terminate the affected Services on written notice without early termination fees. The vendor must provide transition assistance and return or delete Customer Data in accordance with the DPA.
This language should be adapted by qualified counsel to the governing law, transaction structure, and regulatory environment.
How should buyers respond when an acquisition is announced?
Use a written review process instead of relying on a vendor announcement or account-manager reassurance.
- Collect the full contract set: MSA, order forms, SLA, DPA, security addendum, privacy notice, and incorporated online terms.
- Map the transaction: Determine whether the legal entity, ownership, assets, hosting environment, or subprocessors will change.
- Compare commitments: Record current uptime, support targets, pricing, renewal dates, data locations, and termination rights.
- Request a transition statement: Ask who will operate the service, where data will be processed, and whether any terms or controls will change.
- Test exit readiness: Confirm export format, API access, retention period, migration assistance, and deletion evidence.
- Escalate material gaps: Involve legal, security, procurement, and the business owner before signing amended terms or renewing.
This review also reveals whether the agreement has broader weaknesses. For example, a buyer may discover that the contract lacks a clear exit path, weakly defines data ownership, or allows unilateral changes through online terms. The SaaS vendor lock-in exit strategy framework can help turn those findings into a practical migration plan.
Frequently asked questions
Does an acquisition automatically terminate a SaaS contract?
Usually not. The result depends on the transaction structure and the contract’s assignment and change-of-control language. An acquisition may preserve the original agreement while still creating new operational, security, or commercial risks.
Can a customer demand a new contract after an acquisition?
A customer can request amended terms, but the vendor may not be legally required to renegotiate unless the existing agreement provides a consent, termination, or material-change right. Use the announcement as a trigger for structured review.
Should change of control always give the buyer a termination right?
Not necessarily. A conditional right is often more commercially realistic: termination applies when the transaction causes a defined material adverse change, weakens security, reduces service quality, or transfers the contract to a materially different risk profile.
What data rights matter most during a vendor transition?
The most important rights are continued access, export in a usable format, reasonable migration support, clear deletion deadlines, and evidence of deletion. These should apply even if the vendor discontinues the product or transfers operations.
Is source code escrow enough protection?
Not for most SaaS buyers. Escrow may help in certain failure scenarios, but it does not replace data export, transition assistance, continuity obligations, or a workable exit plan. Consider SaaS source code escrow clause protections as one layer within a broader resilience strategy.
A merger or acquisition should be treated as a contract-control event, not merely a corporate announcement. Buyers that define change of control, preserve SLA performance, restrict new data uses, and secure transition assistance are better positioned to accept a transaction—or exit without operational surprise.
Keep reading
Enterprise AI Contract Clauses for Proprietary Data Protection
Enterprise AI contract clauses for proprietary data protection should control training, retention, subprocessors, deletion, and model changes. Use this buyer guide to negotiate stronger terms.
Negotiate Commercial LLM Customer Data Usage Rights
Negotiate commercial LLM customer data usage rights with practical clauses for training opt-outs, retention, subprocessors, deletion, and audit rights. Use this buyer playbook to strengthen your next AI contract.
How to Justify Software Expense to CFO: Build a Finance-Ready Business Case
Learn how to justify software expense to CFOs with a practical ROI, TCO, payback, risk, and adoption model. Build a business case finance can approve.