SaaS Vendor Source Code Escrow Clause: Buyer Negotiation Guide
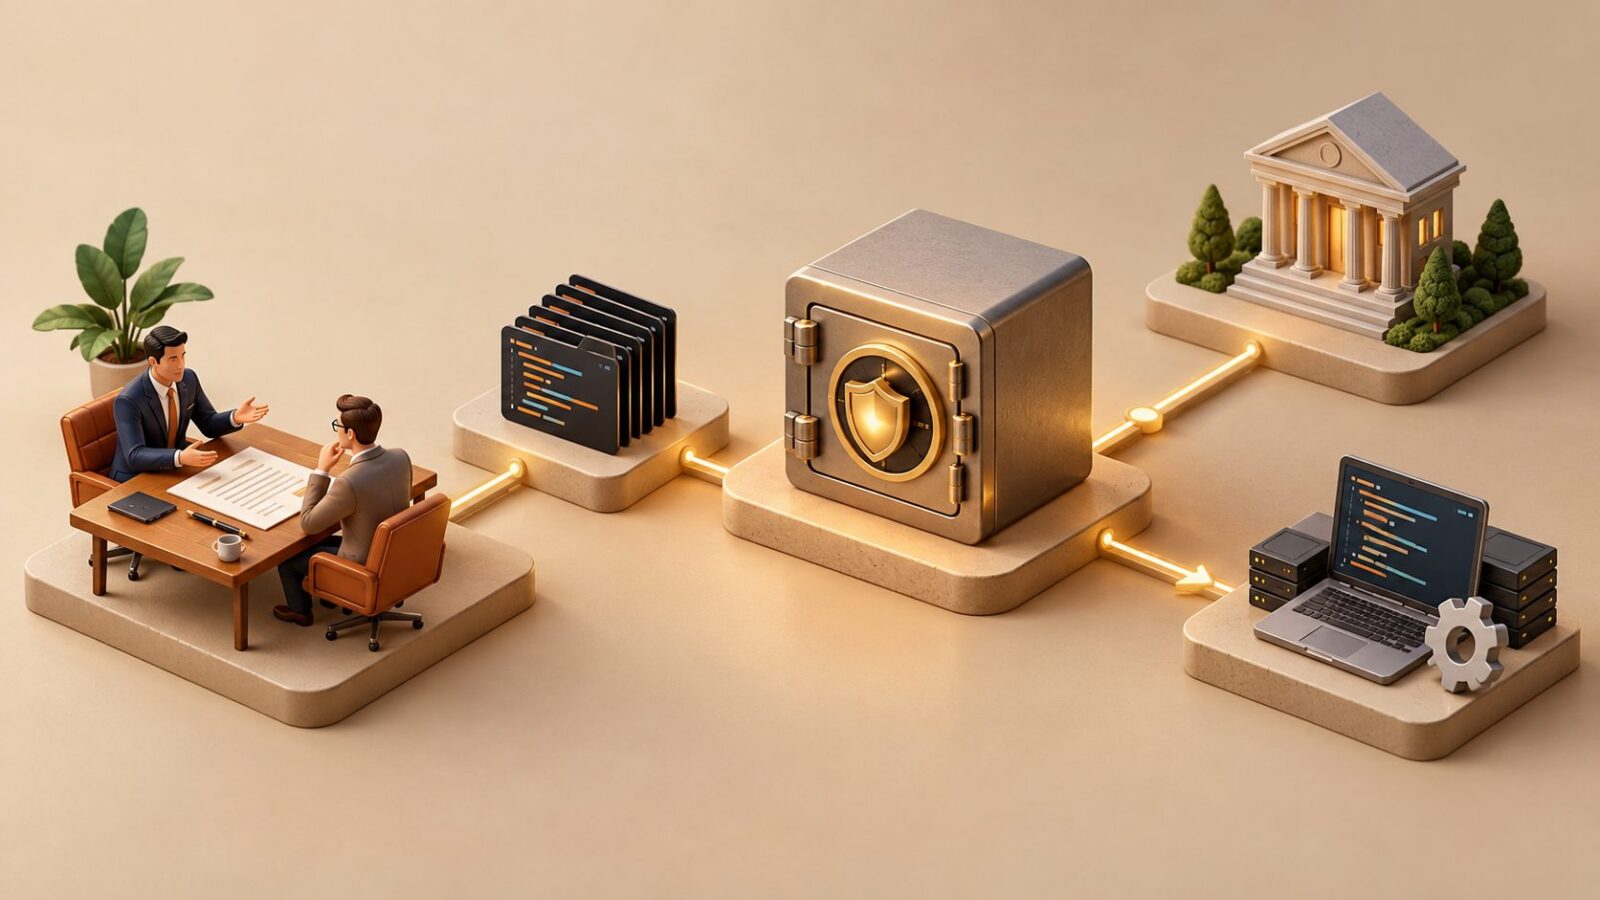
A SaaS vendor source code escrow clause should cover code, cloud deployment, data export, testing, and release triggers. Use this buyer checklist to negotiate continuity protection.
Give every company a team of top closers
A SaaS vendor source code escrow clause should cover code, cloud deployment, data export, testing, and release triggers. Use this buyer checklist to negotiate continuity protection.
Learn the SaaS contract breach cure period standard, including 5-, 10-, 15-, and 30-day benchmarks, carve-outs, notice rules, and buyer protections.
SaaS grandfathered pricing policy review for buyers: identify hidden repricing triggers, test renewal language, and negotiate defensible price protection.
Use this software purchase justification email template to explain ROI, TCO, alternatives, risks, and the exact approval needed. Copy the framework.
SaaS vendor SOC 2 bridge letter review guidance for buyers: verify dates, scope, control changes, incidents, exceptions, and follow-up evidence. Use the checklist.
Learn how to calculate SaaS hard savings, cost avoidance, and realized value with defensible baselines, formulas, controls, and an executive reporting model.
AI software vendor model training data opt out explained for SaaS buyers, with DPA redlines, verification steps, and a practical vendor scorecard.
Spot red flags in SaaS vendor agreements before signing, from renewal traps and price increases to data rights, liability gaps, and exit costs.
Use this SaaS MSA negotiation checklist for buyers to review pricing, data, SLAs, liability, indemnity, renewal, and exit terms before signing.
Use this SaaS vendor IP indemnification scope checklist to test covered claims, exclusions, defense rights, remedies, caps, and third-party risk before signing.