SaaS MSA Negotiation Checklist for Buyers
By toppp.ai | Published 2026-10-14 | Updated 2026-10-14
A SaaS MSA negotiation checklist for buyers should do more than list standard contract sections. It should connect each clause to a business risk, define the evidence needed to enforce it, and identify the remedy if the vendor fails. The highest-value review areas are scope, pricing, data, security, service levels, liability, indemnification, renewal, and exit.
Legal note: This checklist provides commercial contracting guidance, not legal advice. Qualified counsel should adapt the language to the transaction, governing law, industry, and data involved.
What should buyers review first in a SaaS MSA?
Buyers should review the provisions that are expensive or difficult to fix after implementation. A useful priority order is: data access, service continuity, financial exposure, price control, and termination rights. These issues often matter more than cosmetic wording or minor liability definitions.
A SaaS master services agreement usually works with order forms, service-level agreements, data processing terms, security exhibits, and online policies. The contract should state which document controls when terms conflict. For example, an order form may control pricing, while the data processing agreement should control personal-data obligations.
The five-minute risk triage
Before a full redline, ask:
- Can the vendor materially change the service or terms without consent?
- Can the buyer retrieve usable data after termination?
- Are service failures tied to credits, escalation, or termination rights?
- Can renewal or usage changes create an unexpected financial increase?
- Does the liability structure match the business impact of a serious failure?
If the answer to any question is unclear, mark the clause as a negotiation priority.
SaaS MSA negotiation checklist: clause-by-clause review
The following checklist focuses on the clauses most likely to affect procurement outcomes and operational risk.
| Clause | Buyer should verify | Negotiation target |
|---|---|---|
| Scope and service description | Products, modules, usage limits, support, exclusions, and dependencies are defined | Attach a clear service description and prevent material reduction of core functionality |
| Order of precedence | MSA, order form, SLA, DPA, security exhibit, and online terms do not conflict | Use subject-specific precedence instead of a blanket rule |
| Fees and billing | Subscription metric, overage formula, taxes, invoicing, credits, and payment timing | Require transparent usage records and a dispute window before suspension |
| Price changes | Renewal increases, new fees, minimum commitments, and packaging changes | Cap increases and require advance notice for material commercial changes |
| Data rights | Ownership, processing rights, retention, subprocessors, and return format | Preserve buyer ownership and restrict secondary use |
| Security and privacy | Controls, incident notice, audit evidence, and data-location commitments | Put measurable obligations in a DPA or security exhibit |
| Service levels | Uptime calculation, exclusions, support response, and maintenance windows | Add service credits and chronic-failure termination rights |
| Intellectual property | Vendor platform, configurations, integrations, and custom work product | Separate background IP from buyer-specific deliverables |
| Indemnification | Infringement, data incidents, confidentiality breaches, and exclusions | Match indemnity scope to risks the vendor controls |
| Liability | General cap, super-caps, exclusions, and direct damages | Negotiate separate caps for high-severity risks |
| Term and renewal | Initial term, auto-renewal, notice deadline, and termination fees | Require practical notice periods and no silent commercial reset |
| Exit and transition | Data export, deletion, assistance, migration, and continued access | Define format, timing, cost, and post-termination support |
This table is a starting point, not a substitute for reading the definitions. A narrow definition of “confidential information,” “security incident,” or “service availability” can quietly weaken several protections at once.
How should buyers negotiate SaaS pricing and renewal terms?
Buyers should negotiate the pricing mechanism, not just the initial discount. A low first-year price can become expensive if the agreement permits uncapped renewal increases, automatic expansion of user counts, retroactive overage charges, or unilateral packaging changes.
Check these points:
- Is pricing based on seats, transactions, consumption, revenue, devices, or another metric?
- Can the vendor audit usage, and how much notice is required?
- Are unused quantities refundable, transferable, or eligible for rollover?
- Does a product-tier change force migration to a more expensive plan?
- How much notice must the vendor provide before renewal pricing changes?
- Are professional services, implementation, premium support, and integrations priced separately?
For multi-year commitments, tie discounts to an explicit commercial exchange. The buyer may offer term certainty in return for a price cap, payment flexibility, renewal protection, or termination rights for material service failure. A SaaS renewal price increase cap negotiation guide can help structure that trade.
A practical “commercial exposure” formula
Estimate the maximum realistic cost, not only the contracted annual fee:
Three-year exposure = committed fees + likely usage expansion + permitted increases + implementation costs + exit costs
This calculation often reveals that a 5% renewal cap is less valuable than a clear definition of billable usage or a prohibition on retroactive overage charges.
What data, security, and privacy terms belong in the MSA?
Data clauses should answer three separate questions: who owns the data, what the vendor may do with it, and how the buyer gets it back. Buyers should avoid relying on a general statement that customer data remains theirs if the vendor also receives broad rights to use it for analytics, model training, advertising, or product development.
Review whether the agreement covers:
- Customer data ownership and permitted processing purposes
- Aggregated, anonymized, and derived data
- Subprocessor approval and notification
- Security controls and evidence, such as audit reports
- Incident notification deadlines and cooperation duties
- Data residency and cross-border transfer requirements
- Retention, deletion, backups, and legal holds
- Export format, export timing, and reasonable transition assistance
For high-impact data events, a general limitation of liability may not provide enough protection. The buyer should evaluate whether a separate cap or uncapped treatment is appropriate for unauthorized disclosure, intentional misconduct, or regulatory exposure. See the SaaS vendor customer data breach indemnity clause guide for a more focused review.
How should buyers negotiate SLA and support language?
An SLA is useful only when its measurement method and remedy are operationally clear. Buyers should distinguish between availability, support responsiveness, incident resolution, and business continuity because a vendor can meet one while failing another.
Confirm:
- The uptime percentage and measurement period
- What counts as downtime
- Whether scheduled maintenance is excluded
- How degraded performance is treated
- Support severity levels and response targets
- Service-credit calculation and claim process
- Escalation contacts for critical incidents
- Repeated-failure or chronic-breach termination rights
Service credits should not be the only remedy for a system that supports a critical workflow. If repeated SLA failures create operational harm, negotiate a right to terminate the affected order form, receive transition assistance, or obtain a prorated refund.
The enterprise software SLA breach penalty clause guide provides a useful framework for connecting missed service levels to practical remedies.
What liability and indemnity positions should SaaS buyers request?
Liability negotiations should follow the risk rather than use a single universal cap. A general cap based on fees paid may be reasonable for ordinary contract performance, but it may be inadequate for risks such as confidentiality breaches, data incidents, infringement, or deliberate misconduct.
Ask:
- Is the cap based on fees paid, fees payable, or fees paid in a defined period?
- Does the cap apply separately to each order form or to the entire relationship?
- Which claims are excluded from the cap?
- Are consequential damages excluded even when they are the predictable result of a data incident?
- Does the vendor defend and pay for third-party infringement claims?
- Are indemnity exclusions so broad that the protection becomes unusable?
- Does the buyer control settlement when its reputation or regulatory position is affected?
A strong buyer position often uses a tiered liability structure: one general cap for ordinary claims, a higher super-cap for defined high-risk claims, and carefully negotiated exclusions for intentional or legally prohibited conduct. The SaaS contract limitation of liability buyer guide covers this structure in more detail.
How can buyers protect termination and exit rights?
Termination language should be reviewed before implementation begins, because switching costs increase once users, integrations, and data workflows depend on the vendor. Buyers should negotiate both termination triggers and post-termination mechanics.
Include:
- Termination for uncured material breach.
- Termination for repeated SLA failure.
- Termination rights after serious security or privacy events.
- A defined convenience-termination option where commercially justified.
- Prorated refunds for prepaid unused services.
- Data export in a documented, usable format.
- A deletion certificate or equivalent confirmation.
- Time-limited transition assistance and stated rates.
- Continued access during a reasonable migration period.
Do not accept “data will be made available” without defining format, delivery method, timing, and responsibility for export costs. The SaaS vendor lock-in exit strategy framework helps buyers turn exit rights into an executable migration plan.
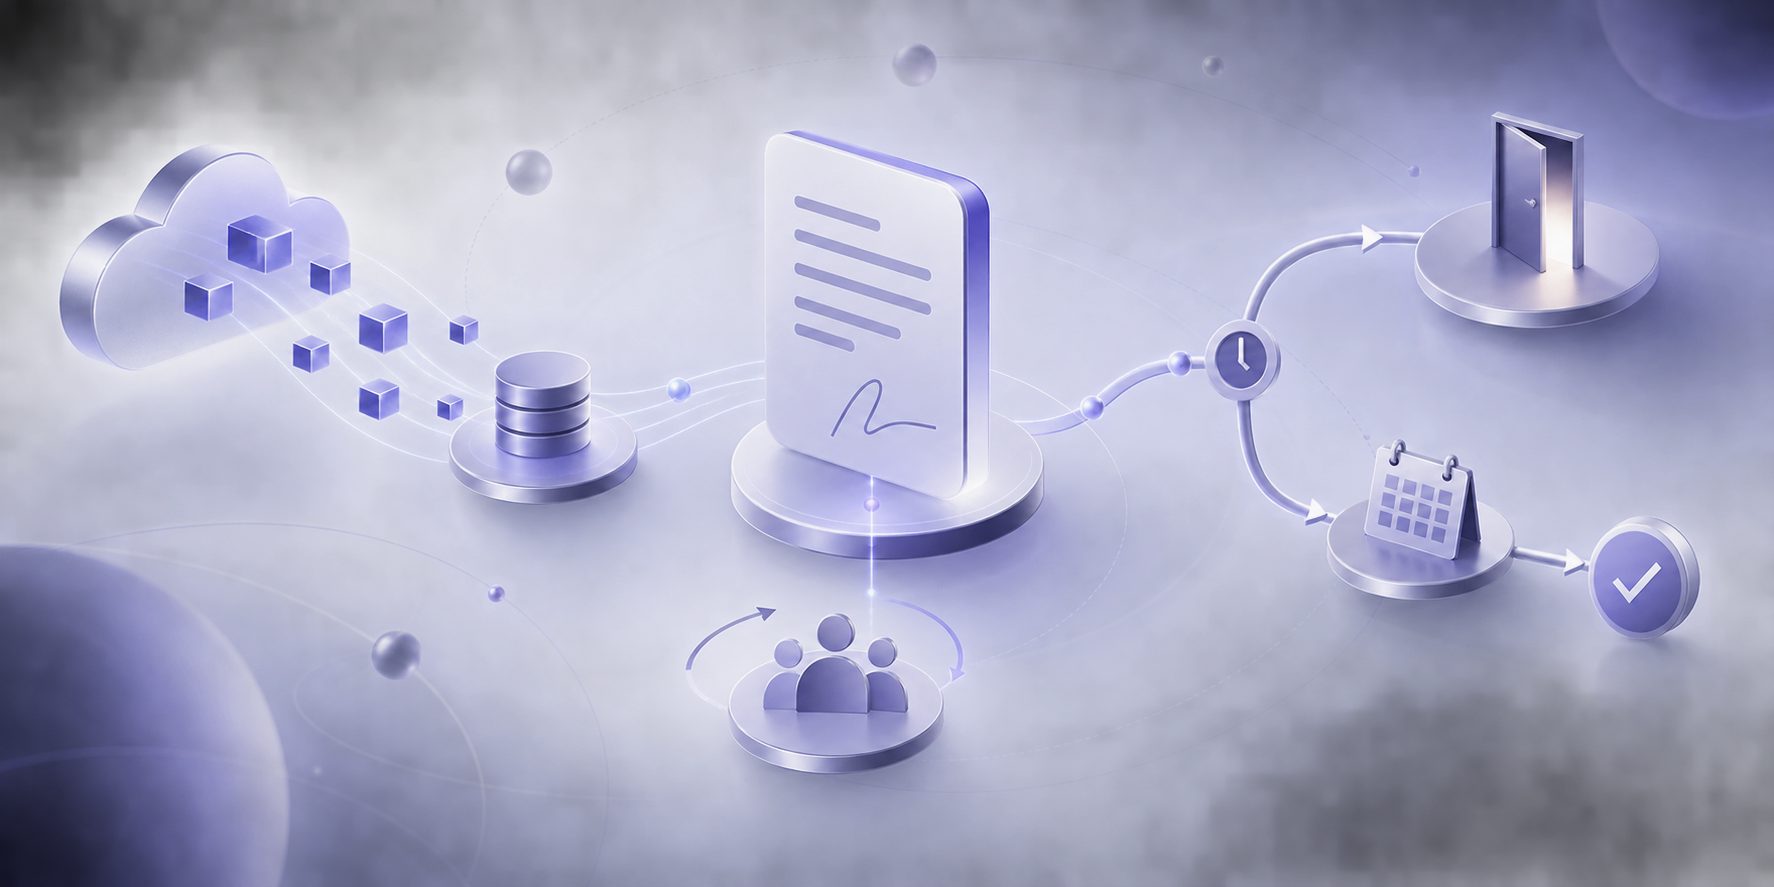
A buyer-friendly negotiation workflow
Use a risk-weighted process instead of sending an unprioritized redline:
- Map the service to business processes. Identify what would stop operations if unavailable.
- Score each clause. Rate impact, likelihood, reversibility, and negotiation effort from 1 to 5.
- Separate must-haves from tradeables. Keep security, data return, and critical remedies distinct from cosmetic preferences.
- Pair every ask with a rationale. Vendors respond better to a defined risk than to unexplained legal language.
- Convert promises into evidence. Add reports, notice periods, response times, calculations, and deliverables.
- Test the exit scenario. Ask who does what on the first business day after termination.
- Record the final position. Store negotiated exceptions with the order form and renewal calendar.
This workflow creates an original reversibility test: if a clause cannot be fixed quickly after signature, negotiate it before purchase. Data export, renewal pricing, liability caps, and service definitions usually score high because they become harder to change after adoption.
Frequently asked questions
Is an MSA the same as a SaaS subscription agreement?
Not always. An MSA typically establishes continuing legal and commercial rules, while order forms specify the purchased service, quantities, term, and price. A vendor may combine both documents, so buyers should focus on the actual hierarchy and incorporated policies.
Which SaaS MSA clause is most important?
There is no universal answer, but data access, service continuity, liability, renewal pricing, and termination usually deserve the closest review because they affect business continuity and total cost.
Should buyers negotiate a separate DPA?
Yes, when the vendor processes personal data or other regulated information. The DPA should identify processing purposes, security duties, subprocessors, incident obligations, retention, and deletion.
Are service credits enough for downtime?
Usually not for business-critical services. Credits can compensate for measurable availability failures, but repeated failures may require escalation, termination rights, refunds, or transition assistance.
When should procurement involve legal and security teams?
Before commercial terms are finalized. Early review exposes non-negotiable risks while the buyer still has leverage and prevents security, privacy, and legal requirements from becoming late-stage blockers.
Keep reading
Red Flags in SaaS Vendor Agreements: A Buyer’s Review Checklist
Spot red flags in SaaS vendor agreements before signing, from renewal traps and price increases to data rights, liability gaps, and exit costs.
SaaS vendor IP indemnification scope checklist: Buyer review guide
Use this SaaS vendor IP indemnification scope checklist to test covered claims, exclusions, defense rights, remedies, caps, and third-party risk before signing.
Enterprise Software Early Termination Payout Clauses: Buyer Guide
Enterprise software early termination payout clauses can combine remaining fees, discounts, and exit costs. Learn the calculation model and negotiation points.