Software Procurement Intake Form Best Practices for Faster Approvals
By toppp.ai | Published 2026-10-07 | Updated 2026-10-07
The most effective software procurement intake form best practices balance two competing needs: making the initial request easy for employees while collecting enough information to route financial, security, privacy, IT, and legal reviews correctly. The form should act as a decision engine—not a long questionnaire that asks every requester to become a procurement expert.
What Is a Software Procurement Intake Form?
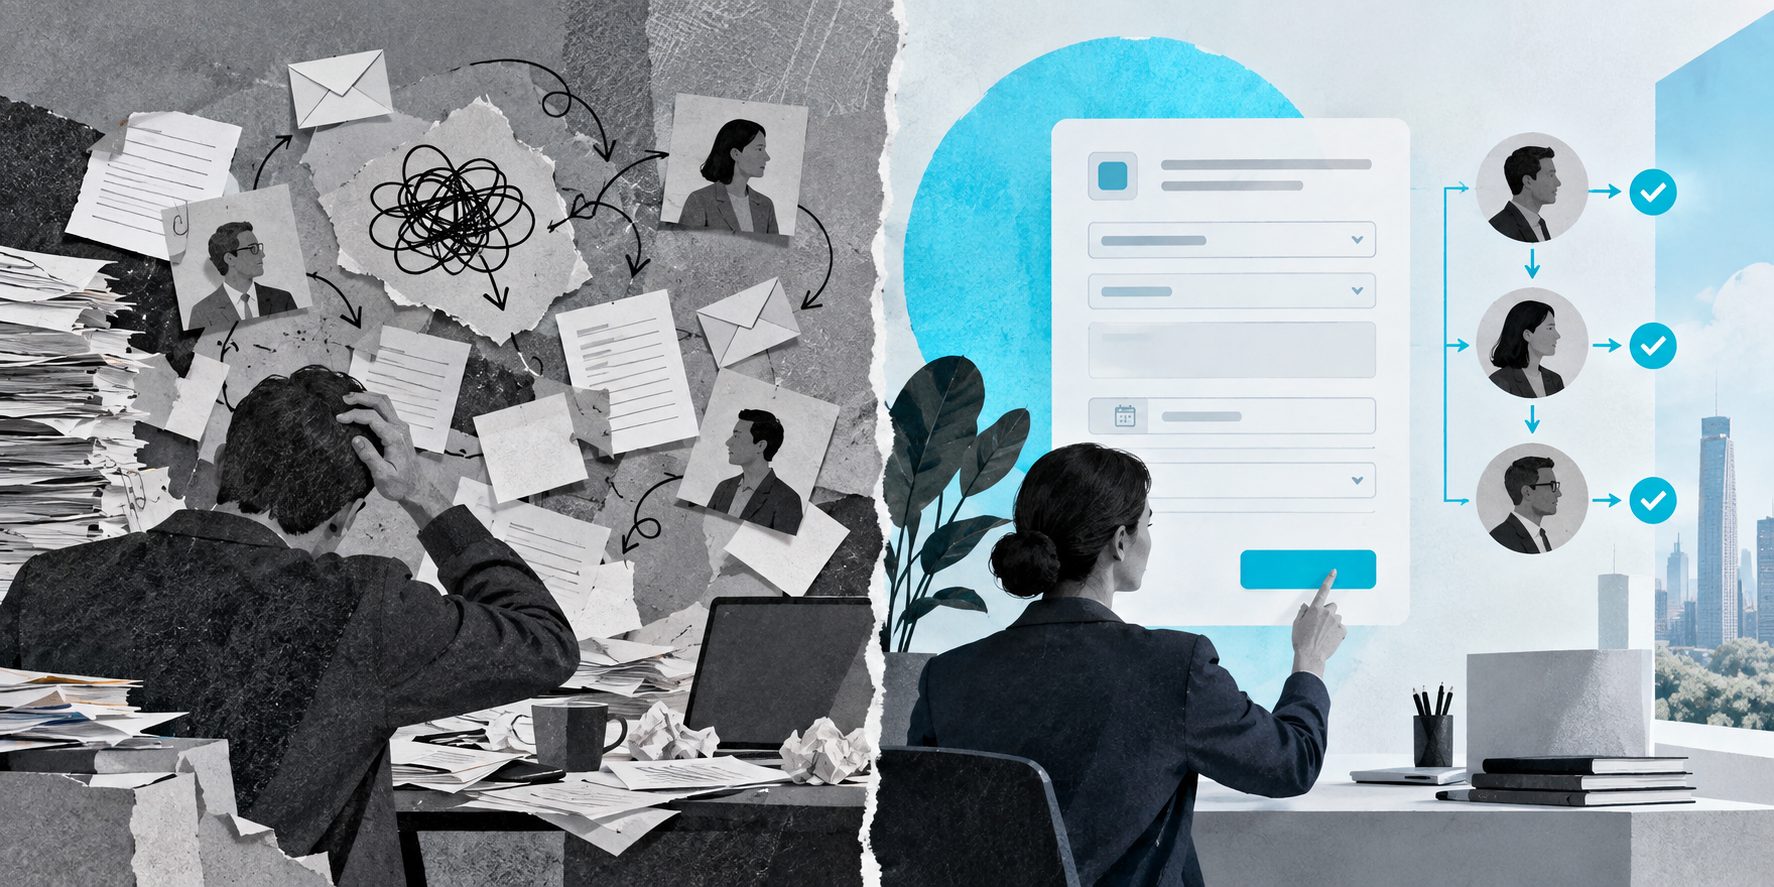
A software procurement intake form is the controlled entry point for requesting a new application, subscription, renewal, trial, or vendor expansion. It captures the business need, expected cost, data exposure, technical dependencies, and timing required to determine who must review the purchase.
The intake form is not the same as a purchase order or vendor security questionnaire. Its purpose is to classify and route the request. Detailed evidence—such as security reports, insurance certificates, contract redlines, and architecture diagrams—should usually be collected after the workflow identifies which reviews apply.
A well-designed form gives procurement one reliable record while showing requesters the current owner, status, next action, and expected timeline. This “single front door” becomes more valuable when connected to a software procurement orchestration platform rather than isolated email and spreadsheet trackers.
Which Fields Should the Initial Form Include?
The initial form should contain only fields needed to identify the request, test for existing alternatives, estimate commercial exposure, and activate the correct workflow. Additional questions should appear conditionally when cost, data, integration, or contract triggers require them.
| Field group | Recommended fields | Decision supported |
|---|---|---|
| Request identity | Requester, department, manager, software name | Ownership and duplicate checking |
| Business need | Problem, intended users, desired outcome | Necessity and solution fit |
| Commercial scope | Estimated users, annual cost, term, budget owner | Spend approval and negotiation |
| Timing | Desired start date, renewal date, urgency reason | Prioritization and sourcing plan |
| Technology | SSO, API, integrations, deployment model | IT and architecture review |
| Data exposure | Data types, personal data, customer data, AI training use | Security and privacy routing |
| Vendor status | New or existing vendor, trial status, vendor contact | Due diligence and contracting |
| Alternatives | Existing tools considered, reason they are insufficient | Consolidation and overlap control |
Use predefined selections where possible, but preserve short free-text fields for business context. For larger requests, attach a structured software procurement business case instead of expanding the intake form indefinitely.
How Should Approval Routing Work?
Approval routing should depend on both financial value and operational risk. A low-cost application processing customer data may require more scrutiny than an expensive renewal that adds no users, integrations, or contractual changes.
A practical routing sequence is:
- Check for duplicates. Compare the requested product and category with the approved software inventory.
- Confirm ownership and budget. Route the request to the manager or budget owner responsible for the outcome.
- Evaluate data and access. Trigger security and privacy review when the vendor handles sensitive data, connects to company systems, or uses AI models.
- Assess technical impact. Involve IT when implementation requires SSO, APIs, data migration, elevated permissions, or support resources.
- Review commercial terms. Send new agreements, material amendments, and nonstandard terms to procurement and legal.
- Record the decision. Preserve approvals, exceptions, conditions, and the accountable software owner.
The workflow should also define delegation, escalation, and return-for-information rules. Otherwise, an absent approver or incomplete answer can leave a request stalled without a visible owner.
What Is the Intake Decision Stack?
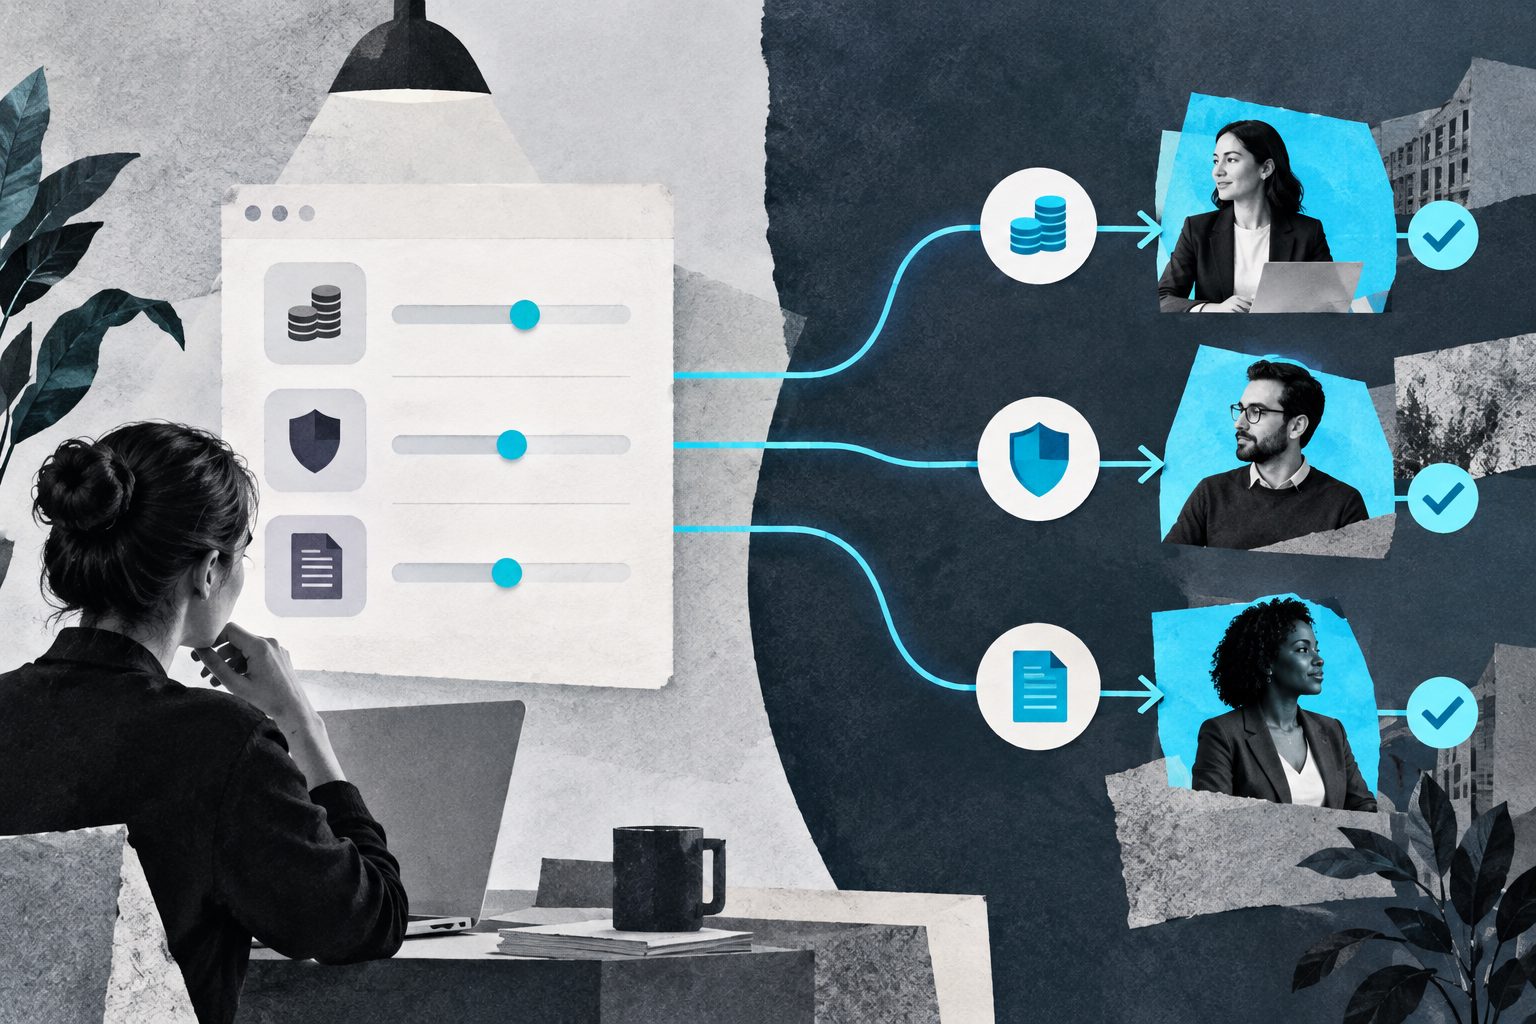
The Intake Decision Stack is a three-layer framework developed for this guide: Signal, Route, and Evidence. It separates what the requester knows from what specialists must verify, reducing unnecessary questions without sacrificing governance.
1. Signal
Signals are simple facts supplied by the requester: expected spend, number of users, data categories, integrations, use case, desired date, and whether the vendor is new. Each signal must influence a decision; otherwise, remove it.
2. Route
Routes convert signals into workflow paths. Examples include budget approval, security assessment, privacy review, architecture review, legal review, competitive sourcing, and executive authorization. One request may activate several routes in parallel.
3. Evidence
Evidence is collected only after a route is triggered. It may include a SOC report, data processing addendum, accessibility documentation, quote, implementation plan, or pricing comparison.
This separation follows the broader principle in CISA’s Secure by Demand Guide: buyers should examine software security before procurement, incorporate requirements during contracting, and continue assessment after purchase.
How Can Teams Prevent Cross-Department Handoffs From Failing?
Cross-functional handoffs fail when teams receive ambiguous requests, repeat questions already answered, or disagree about who owns the next step. Prevent this by assigning one system owner and defining trigger rules jointly with procurement, finance, IT, security, privacy, and legal.
Consider an illustrative request for a $12,000 AI note-taking tool. The requester selects “customer conversations,” “meeting transcripts,” and “vendor trains models using submitted content.” Those three answers should automatically activate privacy, security, and AI vendor review—even if the purchase falls below a normal financial threshold.
The specialist review can then use an AI software vendor due diligence framework without forcing every employee to answer technical questions. The FTC similarly recommends defining how vendors may use, share, retain, and delete company data in written agreements through its vendor security guidance.
How Should Intake Performance Be Measured?
Measure whether the process produces complete, correctly routed decisions—not simply how many forms employees submit. Review performance monthly and examine results by request type, department, spend tier, and risk category.
Track these five operating metrics:
- First-pass completeness: Percentage of requests routed without clarification.
- Time to triage: Time from submission to an assigned workflow and owner.
- Requester wait time: Time blocked on internal reviewers, excluding vendor delays.
- Routing correction rate: Percentage sent to the wrong reviewer or reopened later.
- Duplicate avoidance rate: Requests fulfilled with an existing contract or approved tool.
Also record why requests are returned. If the same missing answer repeatedly causes delays, improve the field label, add an example, or convert the question into a validated selection. Before final approval, compare the full economic impact with an enterprise SaaS total cost of ownership model, especially when implementation, usage, and renewal costs extend beyond the quoted subscription.
Software Procurement Intake Form Best Practices Checklist
Use this checklist before launching or revising the form:
- Provide one clearly advertised submission channel.
- Keep universal questions limited to routing-critical information.
- Use conditional sections for security, privacy, integrations, and legal terms.
- Search the existing software inventory before creating a new request.
- Route by risk and spend rather than spend alone.
- Assign an owner and target response time to every workflow stage.
- Show requesters status, blockers, and the next responsible party.
- Preserve decisions, exceptions, and approval timestamps.
- Review abandoned forms and repeated clarification requests.
- Retire fields that do not affect routing, approval, or reporting.
Frequently Asked Questions
How long should a software procurement intake form be?
It should be short enough for a requester to complete without specialist assistance. Aim for a small universal section followed by conditional questions. Completion time matters less than ensuring every visible field supports a specific decision.
Should security questions appear on the initial form?
Only basic risk-scoping questions should appear initially, such as what data the software handles and whether it connects to internal systems. Detailed security questions should follow when those answers trigger specialist review.
Who should own the software request after approval?
Every approved application should have a named business owner responsible for adoption, license use, renewal decisions, and continued need. IT or procurement may administer the product, but administration does not replace business accountability.
Should renewals use the same intake process?
Renewals should use the same entry point but a different conditional path. The renewal flow should prefill existing contract data and ask about usage, price changes, service issues, scope changes, and cancellation deadlines.
How often should the form be reviewed?
Review it at least quarterly and whenever approval policies, risk standards, or organizational responsibilities change. Analyze routing corrections and clarification requests before adding fields; process problems are not always form problems.
Keep reading
Red Flags in SaaS Vendor Agreements: A Buyer’s Review Checklist
Spot red flags in SaaS vendor agreements before signing, from renewal traps and price increases to data rights, liability gaps, and exit costs.
SaaS MSA Negotiation Checklist for Buyers
Use this SaaS MSA negotiation checklist for buyers to review pricing, data, SLAs, liability, indemnity, renewal, and exit terms before signing.
SaaS vendor IP indemnification scope checklist: Buyer review guide
Use this SaaS vendor IP indemnification scope checklist to test covered claims, exclusions, defense rights, remedies, caps, and third-party risk before signing.