AI Vendor Security Questionnaire Automation: A SaaS Buyer’s Guide
作者:toppp.ai|发布日期:2026-09-20|更新日期:2026-09-20
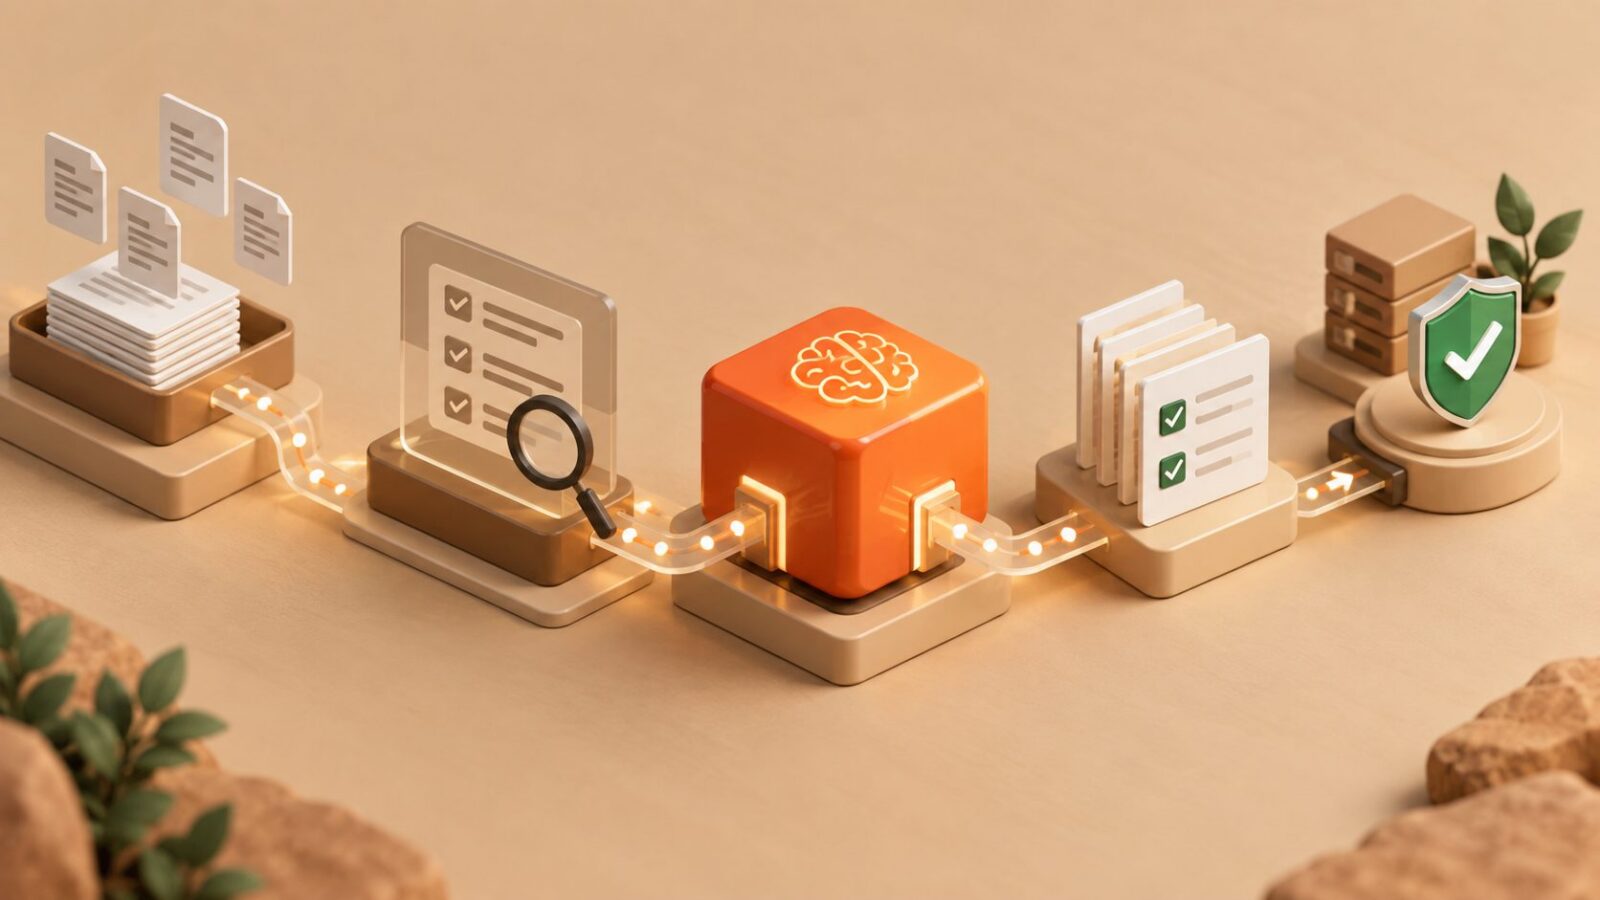
AI vendor security questionnaire automation uses AI to collect, analyze, score, and route vendor security responses. For SaaS procurement teams, the best systems reduce spreadsheet work without turning risk decisions into unverified AI outputs.
Vendor assessments are increasingly complex. A standard security review may now include encryption, access control, subprocessors, data retention, incident response, model training, prompt handling, and autonomous action limits. Automation is useful only when it connects answers to evidence and keeps a qualified reviewer accountable.
What is AI vendor security questionnaire automation?
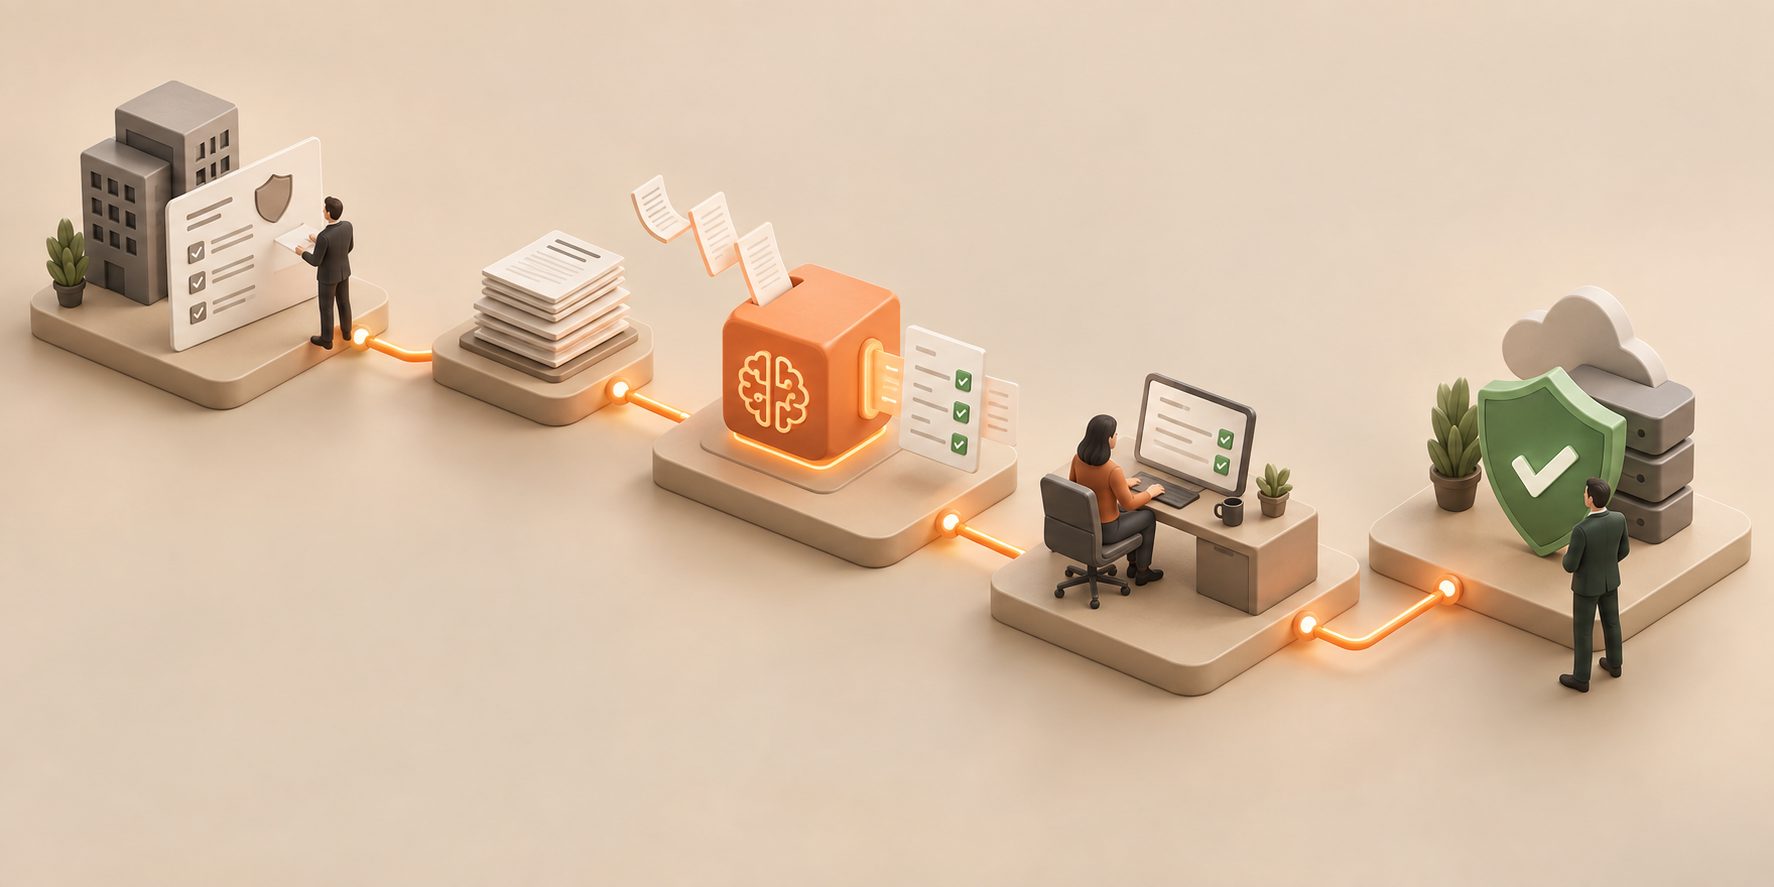
AI vendor security questionnaire automation is software that helps procurement, security, and compliance teams manage vendor questionnaires from intake to decision. It can generate questions, send assessments, extract answers, match responses to evidence, identify gaps, and produce a risk summary.
There are two related use cases:
- Inbound automation: A SaaS provider answers questionnaires sent by customers and prospects.
- Outbound automation: A buyer sends questionnaires to vendors and evaluates the returned evidence.
Several current platforms combine both directions. Market offerings commonly support formats such as Excel, Word, PDF, SIG, CAIQ, DDQ, and hosted portals, while some also provide evidence citations or vendor risk scoring. (wolfia.com)
The distinction matters because the workflow is different. A seller wants accurate, reusable answers that accelerate revenue. A buyer wants independent evidence, risk prioritization, and a defensible approval decision.
Which capabilities should SaaS buyers compare?
The leading automation pages generally emphasize speed, reusable knowledge bases, evidence collection, workflow routing, and portal coverage. Those capabilities are valuable, but they should not be evaluated as one undifferentiated feature list.
| Capability | What it should do | Why it matters |
|---|---|---|
| Questionnaire ingestion | Read Excel, Word, PDF, email, or portal exports | Prevents manual copy-and-paste |
| Answer generation | Draft responses from approved policies and evidence | Reduces repetitive analyst work |
| Evidence mapping | Link each answer to a source document or control | Makes review auditable |
| Confidence scoring | Flag ambiguity, missing evidence, or outdated content | Sends difficult items to experts |
| Vendor risk scoring | Weight criticality, data access, and control gaps | Supports consistent decisions |
| Workflow routing | Assign legal, security, privacy, or procurement tasks | Prevents ownership gaps |
| AI-specific checks | Assess training data, retention, model providers, and autonomy | Covers risks absent from generic questionnaires |
| Change monitoring | Reassess vendors after material product or control changes | Moves beyond annual snapshots |
A common mistake is to buy for answer-generation accuracy alone. A tool may produce fluent answers but still fail if it cannot show where the answer came from, distinguish “unknown” from “no,” or preserve the reviewer’s decision history.
For a broader SaaS procurement workflow, teams can also use a procurement software framework for evaluating sales AI tools to align security review with commercial approval and ownership.
How does automation improve vendor risk assessment?
Automation improves vendor assessment by reducing administrative work and concentrating human attention on exceptions. It does not make a vendor safe merely because a questionnaire has been completed.
The practical value can be understood through four workflow improvements:
- Faster intake: Questions and attachments are normalized into a common structure.
- Less duplication: Similar questions are mapped to previously reviewed answers.
- Better escalation: High-impact gaps go directly to the appropriate specialist.
- More consistent decisions: Vendors are assessed against defined criteria rather than reviewer memory.
Some market vendors claim that automation turns days of drafting into minutes of review or reduces questionnaire response time by 60–80%. These figures are vendor-reported and should not be treated as independent benchmarks. (wolfia.com)
A more useful buyer metric is the review burden per questionnaire:
Review burden = total questions × exception rate × average exception time
For example, a 150-question assessment with a 20% exception rate and 4 minutes per exception creates approximately 120 minutes of specialist review. This model is more actionable than a generic “90% automated” claim because it exposes where the remaining work occurs.
What makes AI vendor questionnaires different?
AI vendors require more than a conventional SOC 2 or infrastructure questionnaire because the risk can exist at the model, data, application, and workflow layers.
A practical AI vendor addendum should ask:
- Is customer data used to train or fine-tune shared models?
- How long are prompts, outputs, logs, and uploaded files retained?
- Which model providers and subprocessors process customer data?
- Can the customer select the model, region, or retention setting?
- What safeguards limit prompt injection, data leakage, or unauthorized actions?
- What human approval is required before the system takes consequential action?
- How are model changes tested and communicated?
- How are harmful, inaccurate, or biased outputs monitored?
- Can customers export or delete their data and configuration?
- What happens if a model provider, API, or critical subprocessor fails?
NIST’s AI Risk Management Framework highlights governance, mapping, measurement, and management as core functions. It also specifically recommends documenting third-party AI systems, monitoring risks, defining contingency processes, and maintaining transparency around data and components. (nist.gov)
This creates an important evaluation rule: an automation tool should help identify unanswered AI governance questions, not merely fill them with generic policy language.
A better framework for comparing automation tools
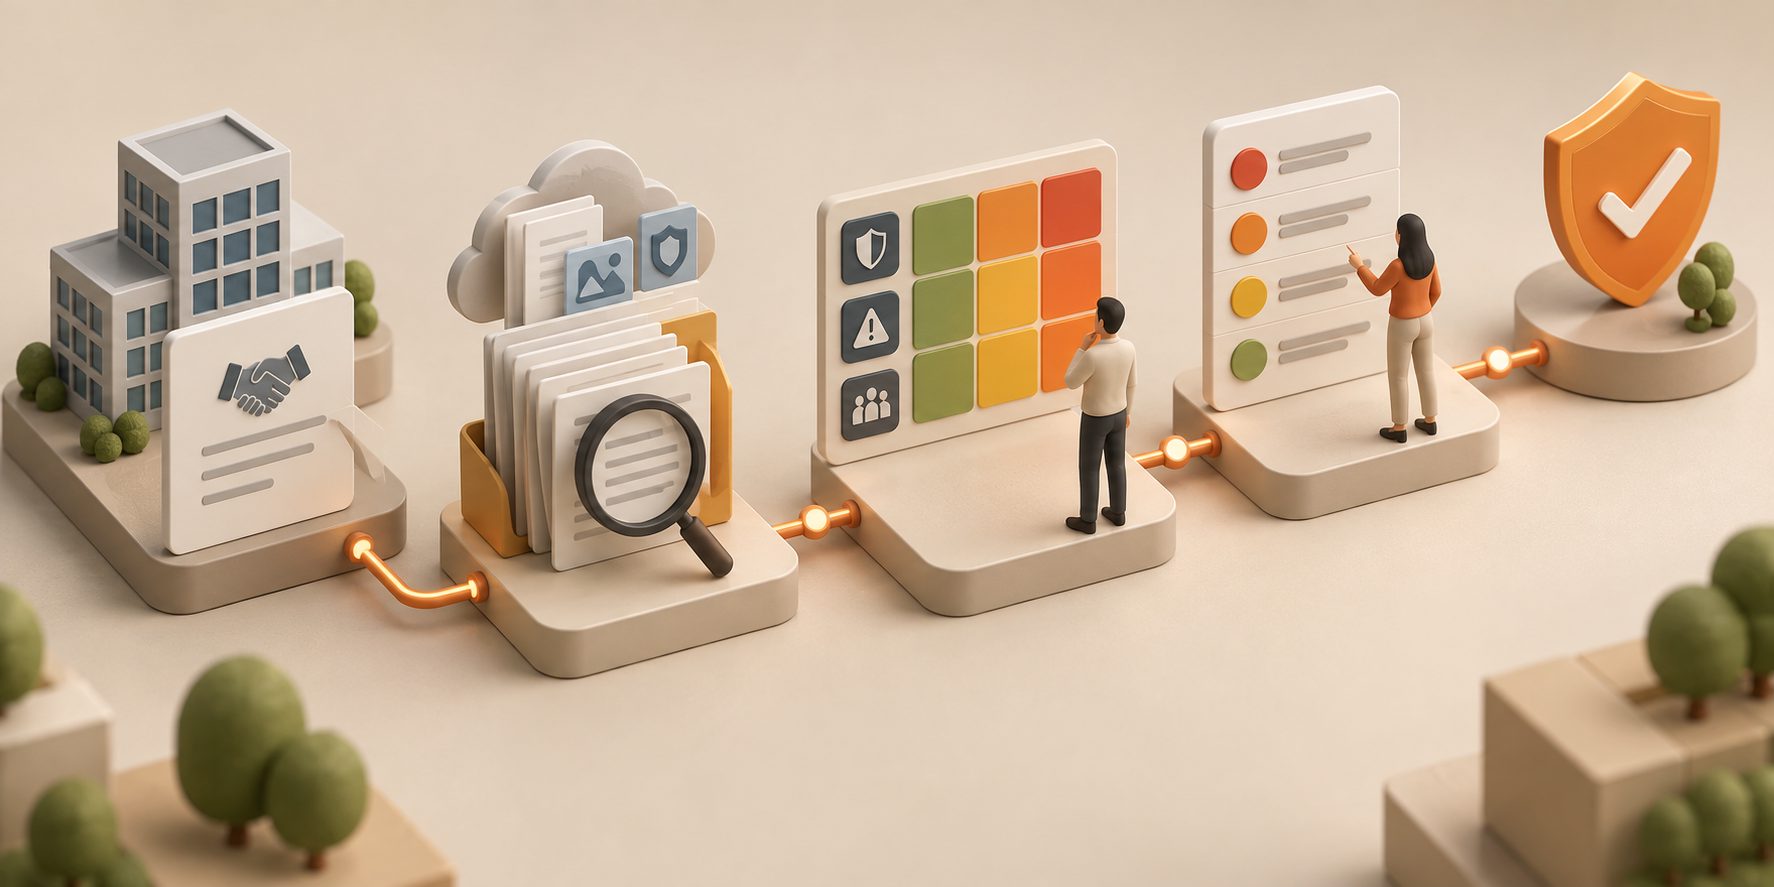
A useful way to compare platforms is the Evidence-to-Decision Framework. Score each vendor or product across three layers:
1. Evidence quality
Can the system locate current, relevant proof?
Check whether it supports:
- Policy and control documents
- SOC reports and certifications
- Penetration test summaries
- Data flow diagrams
- Subprocessor lists
- Contractual commitments
- Product and model documentation
An answer without evidence should be labeled as a draft, not treated as a completed control.
2. Decision quality
Can the platform translate responses into a risk-based recommendation?
Look for configurable treatment such as:
- Approve
- Approve with conditions
- Require remediation
- Escalate for legal or security review
- Reject or defer
Scoring should consider vendor criticality, data sensitivity, privileged access, business dependency, and compensating controls. A missing low-impact policy should not receive the same weight as unrestricted access to production customer data.
3. Governance quality
Can the team explain who approved the vendor, when, and based on what evidence?
Strong governance features include:
- Version history
- Reviewer identity
- Evidence timestamps
- Exception documentation
- Renewal reminders
- Change-triggered reassessment
- Exportable decision records
This framework adds a dimension often underemphasized in product comparisons: the quality of the decision trail. Speed is useful, but procurement teams ultimately need to defend why a vendor was approved.
How should a SaaS team implement automation?
A controlled implementation can follow five steps:
- Define vendor tiers. Separate low-risk tools from vendors handling sensitive data, privileged access, or business-critical workloads.
- Create a minimum evidence standard. Decide which claims require a certification, report, contract clause, technical document, or direct vendor response.
- Build an approved question library. Map recurring questions to controls and risk categories rather than storing isolated answers.
- Set human-review rules. Require specialist review for high-risk gaps, conflicting answers, missing evidence, and AI-specific issues.
- Measure outcomes. Track cycle time, exception rate, overdue reviews, evidence freshness, and the percentage of decisions with documented rationale.
Teams evaluating AI workflow products can also reference an AI sales agent evaluation scorecard for a similar approach to comparing fit, governance, and operational risk.
The goal is not full automation. The goal is selective automation: let software handle repetitive extraction and matching, while humans decide whether residual risk is acceptable.
Frequently asked questions
Can AI complete a vendor security questionnaire without human review?
It can draft and classify many responses, but high-risk answers should receive human review. AI may misread scope, confuse a policy with operational evidence, or infer a control that the vendor has not actually implemented.
Is a SOC 2 report enough for an AI vendor?
Usually not. A SOC 2 report can provide useful evidence about selected controls, but it may not answer questions about model training, prompt retention, AI subprocessors, model changes, or autonomous actions. Those topics typically require additional documentation and contractual review.
What is the difference between vendor risk management and questionnaire automation?
Vendor risk management is the broader program covering intake, inherent risk, due diligence, approval, monitoring, remediation, and offboarding. Questionnaire automation is one workflow component within that program.
How should buyers evaluate AI questionnaire software?
Evaluate evidence grounding, supported file and portal formats, workflow controls, risk customization, AI-specific coverage, auditability, data handling, and the tool’s ability to flag uncertainty. Ask for a live demonstration using a redacted questionnaire and require the vendor to show the evidence behind several answers.
Is the fastest tool always the best option?
No. The best tool reduces review effort while preserving accuracy, traceability, and accountability. A fast system that produces unsupported answers can increase procurement risk rather than reduce it.
Conclusion
AI vendor security questionnaire automation is most valuable when it turns repetitive assessment work into a controlled review process. SaaS buyers should compare more than response speed: they should examine evidence quality, decision logic, AI-specific risk coverage, and the audit trail behind every approval.
The strongest implementation combines automated extraction and matching with risk-based human oversight. That balance helps procurement teams move faster without treating fluent AI output as proof of security.
Keep reading
Red Flags in SaaS Vendor Agreements: A Buyer’s Review Checklist
Spot red flags in SaaS vendor agreements before signing, from renewal traps and price increases to data rights, liability gaps, and exit costs.
SaaS MSA Negotiation Checklist for Buyers
Use this SaaS MSA negotiation checklist for buyers to review pricing, data, SLAs, liability, indemnity, renewal, and exit terms before signing.
SaaS vendor IP indemnification scope checklist: Buyer review guide
Use this SaaS vendor IP indemnification scope checklist to test covered claims, exclusions, defense rights, remedies, caps, and third-party risk before signing.